Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Practice Questions

Exams4sure Dumps

Exam style questions across every 350-701 domain

Last Update 5 hours ago
Total Questions : 801

Start with our free 350-701 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CCNP Security exam. Each 350-701 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

350-701 PDF

350-701 PDF (Printable)
$54.25
$154.99

350-701 Testing Engine

350-701 PDF (Printable)
$59.5
$169.99

350-701 PDF + Testing Engine

350-701 PDF (Printable)
$74.55
$212.99
Question # 151

Which DevSecOps implementation process gives a weekly or daily update instead of monthly or quarterly in the applications?

Options:

A.  

Orchestration

B.  

CI/CD pipeline

C.  

Container

D.  

Security

Discussion 0
Question # 152

Which two global commands must the network administrator implement to limit the attack surface of an internet-facing Cisco router? (Choose two.)

Options:

A.  

no service password-recovery

B.  

no cdp run

C.  

service tcp-keepalives-in

D.  

no ip http server

E.  

ip ssh version 2

Discussion 0
Question # 153

What must be configured on Cisco Secure Endpoint to create a custom detection tile list to detect and quarantine future files?

Options:

A.  

Use the simple custom detection feature and add each detection to the list.

B.  

Add a network IP block allowed list to the configuration and add the blocked files.

C.  

Create an advanced custom detection and upload the hash of each file

D.  

Configure an application control allowed applications list to block the files

Discussion 0
Question # 154

Which metric is used by the monitoring agent to collect and output packet loss and jitter information?

Options:

A.  

WSAv performance

B.  

AVC performance

C.  

OTCP performance

D.  

RTP performance

Discussion 0
Question # 155

When web policies are configured in Cisco Umbrella, what provides the ability to ensure that domains are blocked when they host malware, command and control, phishing, and more threats?

Options:

A.  

Application Control

B.  

Security Category Blocking

C.  

Content Category Blocking

D.  

File Analysis

Discussion 0
Question # 156

Which encryption algorithm provides highly secure VPN communications?

Options:

A.  

3DES

B.  

AES 256

C.  

AES 128

D.  

DES

Discussion 0
Question # 157

A network administrator needs to find out what assets currently exist on the network. Third-party systems need to be able to feed host data into Cisco Firepower. What must be configured to accomplish this?

Options:

A.  

a Network Discovery policy to receive data from the host

B.  

a Threat Intelligence policy to download the data from the host

C.  

a File Analysis policy to send file data into Cisco Firepower

D.  

a Network Analysis policy to receive NetFlow data from the host

Discussion 0
Question # 158

In which two customer environments is the Cisco Secure Web Appliance Virtual connector traffic direction method selected? (Choose two.)

Options:

A.  

Customer needs to support roaming users.

B.  

Customer does not own Cisco hardware and needs Transparent Redirection (WCCP).

C.  

Customer owns ASA Appliance and Virtual Form Factor is required.

D.  

Customer does not own Cisco hardware and needs Explicit Proxy.

E.  

Customer owns ASA Appliance and SSL Tunneling is required.

Discussion 0
Question # 159

How does Cisco Stealthwatch Cloud provide security for cloud environments?

Options:

A.  

It delivers visibility and threat detection.

B.  

It prevents exfiltration of sensitive data.

C.  

It assigns Internet-based DNS protection for clients and servers.

D.  

It facilitates secure connectivity between public and private networks.

Discussion 0
Question # 160

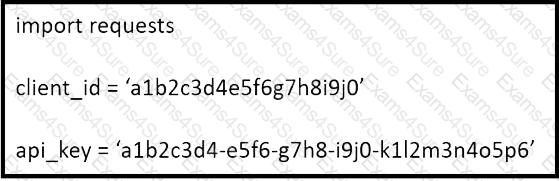
Refer to the exhibit.

Question # 160

What does the API key do while working with https://api.amp.cisco.com/v1/computers?

Options:

A.  

displays client ID

B.  

HTTP authorization

C.  

Imports requests

D.  

HTTP authentication

Discussion 0
Question # 161

An engineer must modify a policy to block specific addresses using Cisco Umbrella. The policy is created already and is actively u: of the default policy elements. What else must be done to accomplish this task?

Options:

A.  

Add the specified addresses to the identities list and create a block action.

B.  

Create a destination list for addresses to be allowed or blocked.

C.  

Use content categories to block or allow specific addresses.

D.  

Modify the application settings to allow only applications to connect to required addresses.

Discussion 0
Question # 162

What are the two types of managed Intercloud Fabric deployment models? (Choose two.)

Options:

A.  

Public managed

B.  

Service Provider managed

C.  

Enterprise managed

D.  

User managed

E.  

Hybrid managed

Discussion 0
Question # 163

What is a difference between a DoS attack and a DDoS attack?

Options:

A.  

A DoS attack is where a computer is used to flood a server with TCP and UDP packets whereas a DDoS attack is where multiple systems target a single system with a DoS attack

B.  

A DoS attack is where a computer is used to flood a server with TCP and UDP packets whereas a DDoS attack is where a computer is used to flood multiple servers that are distributed over a LAN

C.  

A DoS attack is where a computer is used to flood a server with UDP packets whereas a DDoS attack is where a computer is used to flood a server with TCP packets

D.  

A DoS attack is where a computer is used to flood a server with TCP packets whereas a DDoS attack is where a computer is used to flood a server with UDP packets

Discussion 0
Question # 164

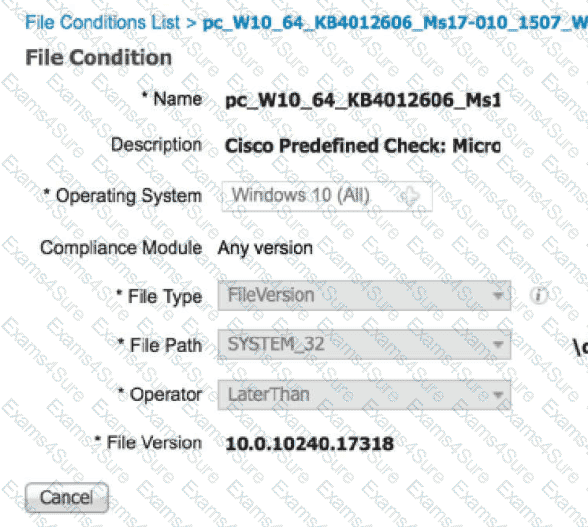
An engineer used a posture check on a Microsoft Windows endpoint and discovered that the MS17-010 patch

was not installed, which left the endpoint vulnerable to WannaCry ransomware. Which two solutions mitigate

the risk of this ransom ware infection? (Choose two)
Options:

A.  

Configure a posture policy in Cisco Identity Services Engine to install the MS17-010 patch before allowingaccess on the network.

B.  

Set up a profiling policy in Cisco Identity Service Engine to check and endpoint patch level before allowingaccess on the network.

C.  

Configure a posture policy in Cisco Identity Services Engine to check that an endpoint patch level is metbefore allowing access on the network.

D.  

Configure endpoint firewall policies to stop the exploit traffic from being allowed to run and replicatethroughout the network.

E.  

Set up a well-defined endpoint patching strategy to ensure that endpoints have critical vulnerabilities patched in a timely fashion.

Discussion 0
Question # 165

An organization is implementing URL blocking using Cisco Umbrella. The users are able to go to some sites

but other sites are not accessible due to an error. Why is the error occurring?

Options:

A.  

Client computers do not have the Cisco Umbrella Root CA certificate installed.

B.  

IP-Layer Enforcement is not configured.

C.  

Client computers do not have an SSL certificate deployed from an internal CA server.

D.  

Intelligent proxy and SSL decryption is disabled in the policy

Discussion 0

Free Exams Sample Questions