Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Practice Questions

Question # 91

Which two solutions help combat social engineering and phishing at the endpoint level? (Choose two.)

Options:

A.  

Cisco Umbrella

B.  

Cisco ISE

C.  

Cisco DNA Center

D.  

Cisco TrustSec

E.  

Cisco Duo Security

Discussion 0
Question # 92

Which endpoint solution protects a user from a phishing attack?

Options:

A.  

Cisco Identity Services Engine

B.  

Cisco AnyConnect with ISE Posture module

C.  

Cisco AnyConnect with Network Access Manager module

D.  

Cisco AnyConnect with Umbrella Roaming Security module

Discussion 0
Question # 93

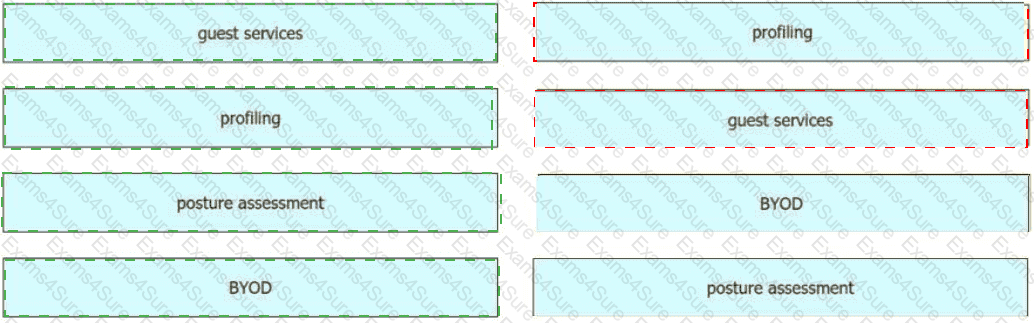
Drag and drop the concepts from the left onto the correct descriptions on the right
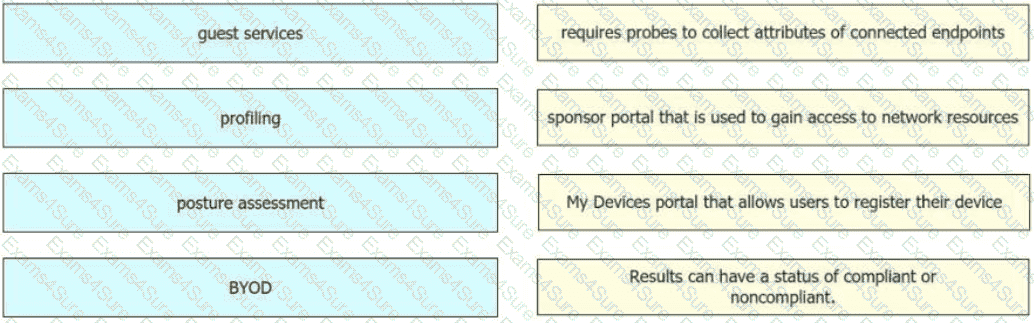
Question # 93

Options:

Discussion 0
Question # 94

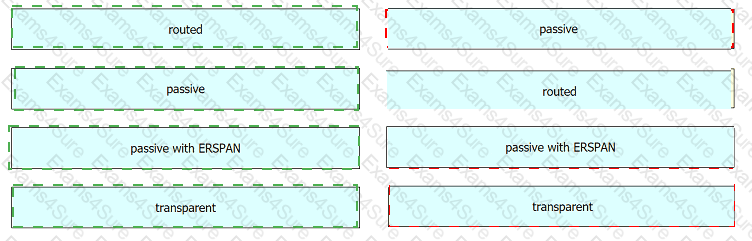
Drag and drop the deployment models from the left onto the explanations on the right.
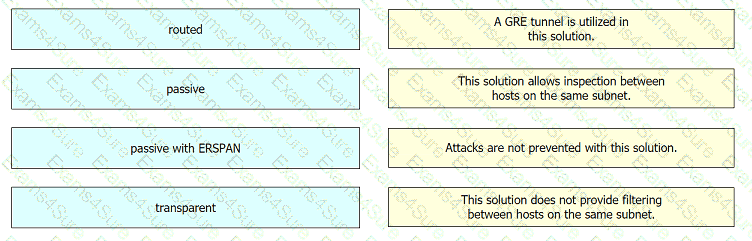
Question # 94

Options:

Discussion 0
Question # 95

An engineer is configuring AMP for endpoints and wants to block certain files from executing. Which outbreak

control method is used to accomplish this task?

Options:

A.  

device flow correlation

B.  

simple detections

C.  

application blocking list

D.  

advanced custom detections

Discussion 0
Question # 96

Which Cisco security solution secures public, private, hybrid, and community clouds?

Options:

A.  

Cisco ISE

B.  

Cisco ASAv

C.  

Cisco Cloudlock

D.  

Cisco pxGrid

Discussion 0
Question # 97

A network engineer has entered the snmp-server user andy myv3 auth sha cisco priv aes 256

cisc0380739941 command and needs to send SNMP information to a host at 10.255.254.1. Which command achieves this goal?

Options:

A.  

snmp-server host inside 10.255.254.1 version 3 andy

B.  

snmp-server host inside 10.255.254.1 version 3 myv3

C.  

snmp-server host inside 10.255.254.1 snmpv3 andy

D.  

snmp-server host inside 10.255.254.1 snmpv3 myv3

Discussion 0
Question # 98

Which cloud service offering allows customers to access a web application that is being hosted, managed, and maintained by a cloud service provider?

Options:

A.  

IaC

B.  

SaaS

C.  

IaaS

D.  

PaaS

Discussion 0
Question # 99

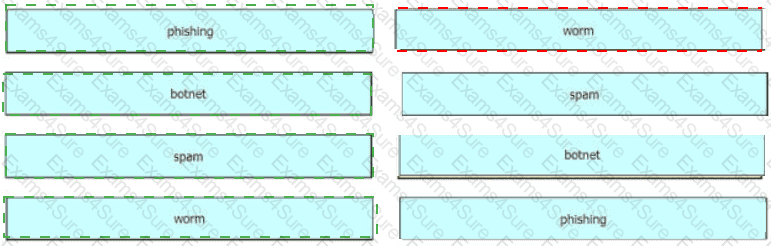
Drag and drop the common security threats from the left onto the definitions on the right.
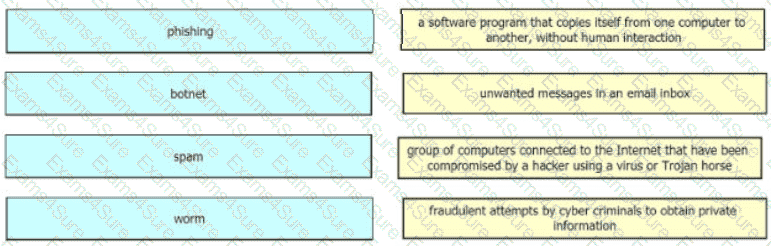
Question # 99

Options:

Discussion 0
Question # 100

Refer to the exhibit.

=== Cisco Secure Endpoint - Detection Event ===

Endpoint : LAB-WKSTN-047 User: user1

Policy Group : Lab-Workstations Mode: Audit

Engine : ETHOS (fuzzy fingerprint)

Disposition : Malicious

File : C:\Users\user1\AppData\Local\Temp\svchost32.exe

SHA256 : 3a9f2c1d...e881b4a7

Parent Process: winword.exe

Threat Name : W32.Trojan.GenericK

D.  

Agent

Retrospective : Previously UNKNOWN

Disposition changed to MALICIOUS at 09:31:55 UTC

File Activity : Created, Executed

Network : TCP outbound - > 91.205.188.47:4444

DNS query: c2-update.pharmadomain.ru

Quarantine : NOT quarantined (Audit mode active)

A security analyst at a pharmaceutical company is reviewing a Cisco Secure Endpoint malware-detection alert triggered on a laboratory workstation. The analyst observes the event data above. Which two things are occurring? (Choose two.)

Options:

A.  

The antivirus engine update interval on workstation LAB-WKSTN-047 is too infrequent.

B.  

The endpoint is running in Audit mode; the file was detected but not quarantined.

C.  

The endpoint is running in Audit mode; the file was detected and quarantined.

D.  

The file executed, was spawned by winword.exe, and opened an outbound connection to external command-and-control infrastructure.

E.  

The parent file winword.exe is on a custom application allow list, permitting the malicious file to execute.

Discussion 0
Question # 101

Which two Cisco ISE components must be configured for BYOD? (Choose two.)

Options:

A.  

local WebAuth

B.  

central WebAuth

C.  

null WebAuth

D.  

guest

E.  

dual

Discussion 0
Question # 102

A manufacturing company contracted an external software vendor to develop an application that dynamically creates marketing messages personalized to the business and audience. To ensure that communication between the sender and recipient email addresses does not create false positives, an exception rule must be configured in Cisco Secure Email Threat Defense. Which configuration must be performed?

Options:

A.  

Implement an Exception Rule with a wildcard email address.

B.  

Add a Policy Exception Rule with a Sender/Recipient pair set.

C.  

Apply a sender-based Policy Exception Rule.

D.  

Configure a recipient-based Policy Exception Rule.

Discussion 0
Question # 103

Which two parameters are used to prevent a data breach in the cloud? (Choose two.)

Options:

A.  

DLP solutions

B.  

strong user authentication

C.  

encryption

D.  

complex cloud-based web proxies

E.  

antispoofing programs

Discussion 0
Question # 104

Which two features are used to configure Cisco ESA with a multilayer approach to fight viruses and malware?

(Choose two)

Options:

A.  

Sophos engine

B.  

white list

C.  

RAT

D.  

outbreak filters

E.  

DLP

Discussion 0
Question # 105

Which type of DNS abuse exchanges data between two computers even when there is no direct connection?
Options:

A.  

Malware installation

B.  

Command-and-control communication

C.  

Network footprinting

D.  

Data exfiltration

Discussion 0

350-701 PDF

350-701 PDF (Printable)
$46.5
$154.99

350-701 Testing Engine

350-701 PDF (Printable)
$51
$169.99

350-701 PDF + Testing Engine

350-701 PDF (Printable)
$63.9
$212.99

Free Exams Sample Questions