Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Practice Questions

Exams4sure Dumps

Exam style questions across every 350-701 domain

Last Update 4 hours ago
Total Questions : 801

Start with our free 350-701 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CCNP Security exam. Each 350-701 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

350-701 PDF

350-701 PDF (Printable)
$54.25
$154.99

350-701 Testing Engine

350-701 PDF (Printable)
$59.5
$169.99

350-701 PDF + Testing Engine

350-701 PDF (Printable)
$74.55
$212.99
Question # 106

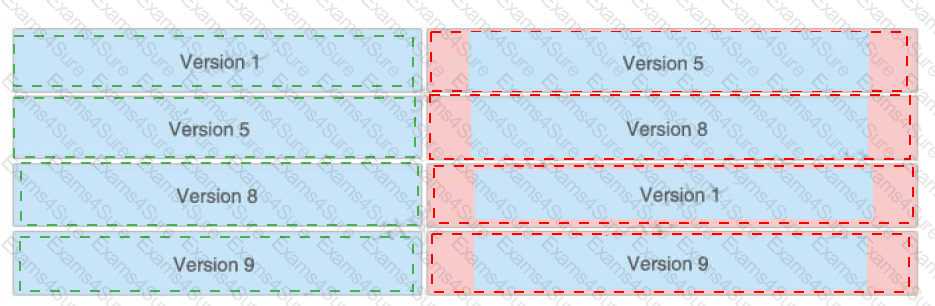
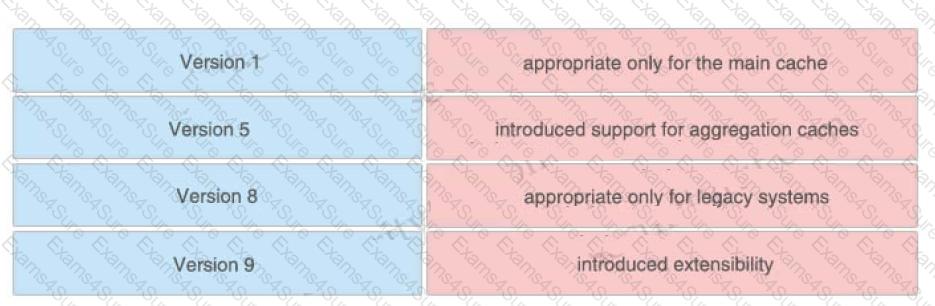
Drag and drop the NetFlow export formats from the left onto the descriptions on the right.
Question # 106

Options:

Discussion 0
Question # 107

In which scenario is endpoint-based security the solution?

Options:

A.  

inspecting encrypted traffic

B.  

device profiling and authorization

C.  

performing signature-based application control

D.  

inspecting a password-protected archive

Discussion 0
Question # 108

An organization recently installed a Cisco WSA and would like to take advantage of the AVC engine to allow the organization to create a policy to control application specific activity. After enabling the AVC engine, what must be done to implement this?

Options:

A.  

Use security services to configure the traffic monitor, .

B.  

Use URL categorization to prevent the application traffic.

C.  

Use an access policy group to configure application control settings.

D.  

Use web security reporting to validate engine functionality

Discussion 0
Question # 109

A network engineer is trying to figure out whether FlexVPN or DMVPN would fit better in their environment.

They have a requirement for more stringent security multiple security associations for the connections, more efficient VPN establishment as well consuming less bandwidth. Which solution would be best for this and why?

Options:

A.  

DMVPN because it supports IKEv2 and FlexVPN does not

B.  

FlexVPN because it supports IKEv2 and DMVPN does not

C.  

FlexVPN because it uses multiple SAs and DMVPN does not

D.  

DMVPN because it uses multiple SAs and FlexVPN does not

Discussion 0
Question # 110

Which network monitoring solution uses streams and pushes operational data to provide a near real-time view

of activity?

Options:

A.  

SNMP

B.  

SMTP

C.  

syslog

D.  

model-driven telemetry

Discussion 0
Question # 111

Refer to the exhibit.

Question # 111

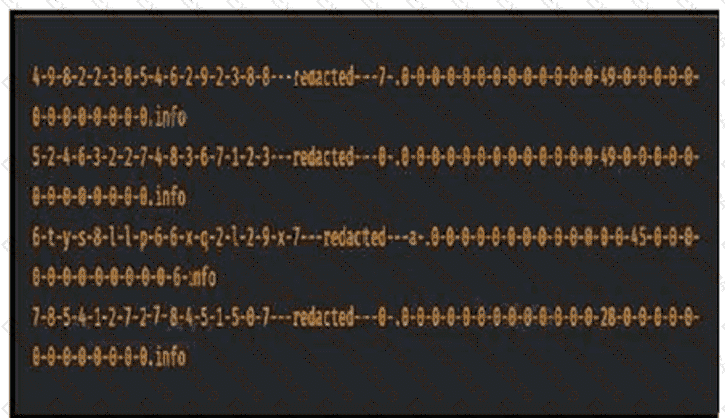
Consider that any feature of DNS requests, such as the length off the domain name

and the number of subdomains, can be used to construct models of expected behavior to which

observed values can be compared. Which type of malicious attack are these values associated with?

Options:

A.  

Spectre Worm

B.  

Eternal Blue Windows

C.  

Heartbleed SSL Bug

D.  

W32/AutoRun worm

Discussion 0
Question # 112

An organization uses Cisco FMC to centrally manage multiple Cisco FTD devices The default management port conflicts with other communications on the network and must be changed What must be done to ensure that all devices can communicate together?

Options:

A.  

Set the sftunnel to go through the Cisco FTD

B.  

Change the management port on Cisco FMC so that it pushes the change to all managed Cisco FTD devices

C.  

Set the sftunnel port to 8305.

D.  

Manually change the management port on Cisco FMC and all managed Cisco FTD devices

Discussion 0
Question # 113

What is an advantage of network telemetry over SNMP pulls?

Options:

A.  

accuracy

B.  

encapsulation

C.  

security

D.  

scalability

Discussion 0
Question # 114

Refer to the exhibit.

Question # 114

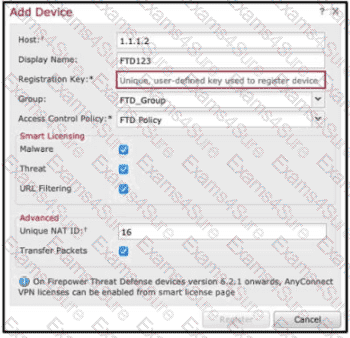
An administrator is adding a new Cisco FTD device to their network and wants to manage it with Cisco FM

C.  

The Cisco FTD is not behind a NAT device. Which command is needed to enable this on the Cisco FTD?

Options:

A.  

configure manager add DONTRESOLVE kregistration key >

B.  

configure manager add < FMC IP address > < registration key > 16

C.  

configure manager add DONTRESOLVE < registration key > FTD123

D.  

configure manager add < FMC IP address > < registration key >

Discussion 0
Question # 115

What are two list types within AMP for Endpoints Outbreak Control? (Choose two)

Options:

A.  

blocked ports

B.  

simple custom detections

C.  

command and control

D.  

allowed applications

E.  

URL

Discussion 0
Question # 116

What is the function of SDN southbound API protocols?

Options:

A.  

to allow for the dynamic configuration of control plane applications

B.  

to enable the controller to make changes

C.  

to enable the controller to use REST

D.  

to allow for the static configuration of control plane applications

Discussion 0
Question # 117

A customer has various external HTTP resources available including Intranet Extranet and Internet, with a

proxy configuration running in explicit mode. Which method allows the client desktop browsers to be configured

to select when to connect direct or when to use the proxy?

Options:

A.  

Transport mode

B.  

Forward file

C.  

PAC file

D.  

Bridge mode

Discussion 0
Question # 118

When a transparent authentication fails on the Web Security Appliance, which type of access does the end user get?

Options:

A.  

guest

B.  

limited Internet

C.  

blocked

D.  

full Internet

Discussion 0
Question # 119

When network telemetry is implemented, what is important to be enabled across all network infrastructure devices to correlate different sources?

Options:

A.  

CDP

B.  

NTP

C.  

syslog

D.  

DNS

Discussion 0
Question # 120

Refer to the exhibit.

Question # 120

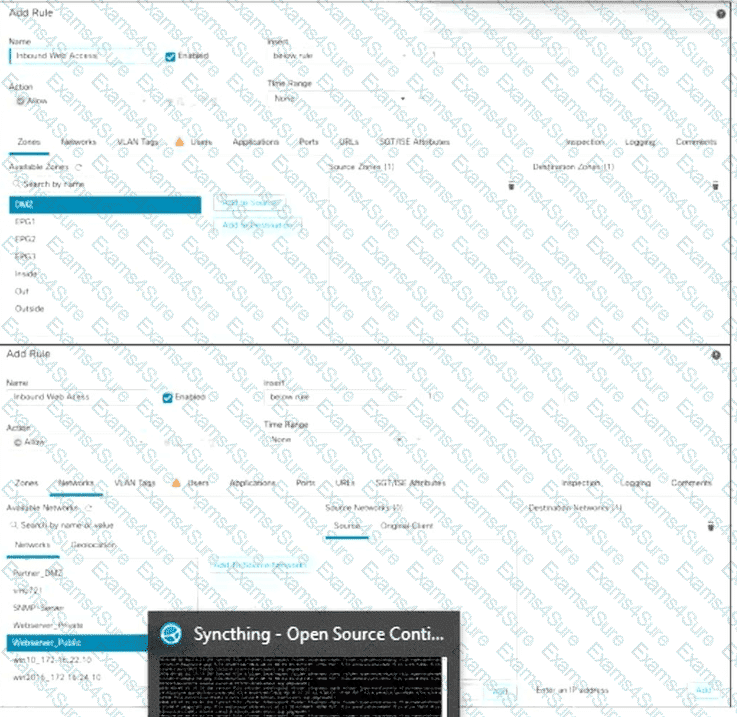
A security engineer is publishing a public web server located in the DMZ of a Cisco Secure Firewall Threat Defense device managed by Cisco Secure Firewall Management Center. The required network objects, Webserver_Private and Webserver_Public, are already defined, and an Auto NAT static rule mapping the public address to the private DMZ address is in place. The web server must be reachable from any source on the Internet. The engineer must configure a new Access Control Rule within the existing Access Control Policy. Which two configuration actions must be performed to meet the requirements? (Choose two.)


Options:

A.  

Add DMZ as the Source Zone and Outside as the Destination Zone.

B.  

Add Webserver_Private as the Source Network and Webserver_Public as the Destination Network.

C.  

Add Any as the Source Network and Webserver_Private as the Destination Network.

D.  

Add Any as the Source Network and Webserver_Public as the Destination Network.

E.  

Add Outside as the Source Zone and DMZ as the Destination Zone.

Discussion 0

Free Exams Sample Questions