

Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Practice Questions

Exams4sure Dumps

Exam style questions across every 350-701 domain

Last Update 5 hours ago
Total Questions : 801

Start with our free 350-701 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CCNP Security exam. Each 350-701 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

350-701 PDF

350-701 PDF (Printable)
$54.25
$154.99

350-701 Testing Engine

350-701 PDF (Printable)
$59.5
$169.99

350-701 PDF + Testing Engine

350-701 PDF (Printable)
$74.55
$212.99
Question # 121

What is the primary role of the Cisco Email Security Appliance?

Options:

A.  

Mail Submission Agent

B.  

Mail Transfer Agent

C.  

Mail Delivery Agent

D.  

Mail User Agent

Discussion 0
Question # 122

When NetFlow is applied to an interface, which component creates the flow monitor cache that is used

to collect traffic based on the key and nonkey fields in the configured record?

Options:

A.  

records

B.  

flow exporter

C.  

flow sampler

D.  

flow monitor

Discussion 0
Question # 123

Which Cisco Firewall solution requires zone definition?

Options:

A.  

CBAC

B.  

Cisco AMP

C.  

ZBFW

D.  

Cisco ASA

Discussion 0
Question # 124

What is a feature of NetFlow Secure Event Logging?

Options:

A.  

It exports only records that indicate significant events in a flow.

B.  

It filters NSEL events based on the traffic and event type through RSVP.

C.  

It delivers data records to NSEL collectors through NetFlow over TCP only.

D.  

It supports v5 and v8 templates.

Discussion 0
Question # 125

What are two benefits of Flexible NetFlow records? (Choose two)

Options:

A.  

They allow the user to configure flow information to perform customized traffic identification

B.  

They provide attack prevention by dropping the traffic

C.  

They provide accounting and billing enhancements

D.  

They converge multiple accounting technologies into one accounting mechanism

E.  

They provide monitoring of a wider range of IP packet information from Layer 2 to 4

Discussion 0
Question # 126

Which command is used to log all events to a destination colector 209.165.201.107?
Options:

A.  

CiscoASA(config-pmap-c)#flow-export event-type flow-update destination 209.165.201.10

B.  

CiscoASA(config-cmap)# flow-export event-type all destination 209.165.201.

C.  

CiscoASA(config-pmap-c)#flow-export event-type all destination 209.165.201.10

D.  

CiscoASA(config-cmap)#flow-export event-type flow-update destination 209.165.201.10

Discussion 0
Question # 127

Question # 127

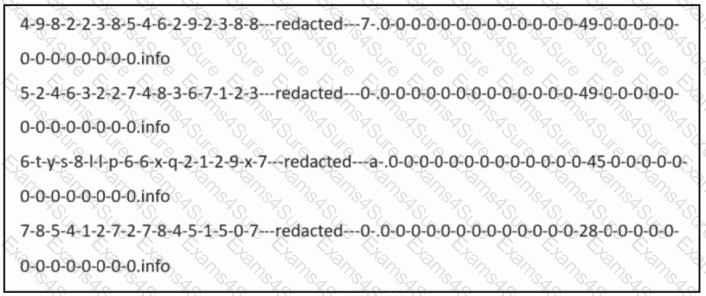
Refer to the exhibit. Consider that any feature of DNS requests, such as the length of the domain name and the number of subdomains, can be used to construct models of expected behavior to which observed values can be compared. Which type of malicious attack are these values associated with?

Options:

A.  

W32/AutoRun worm

B.  

HeartBleed SSL Bug

C.  

Spectre Worm

D.  

Eternal Blue Windows

Discussion 0
Question # 128

On which part of the IT environment does DevSecOps focus?

Options:

A.  

application development

B.  

wireless network

C.  

data center

D.  

perimeter network

Discussion 0
Question # 129

A network engineer must create an access control list on a Cisco Adaptive Security Appliance firewall. The access control list must permit HTTP traffic to the internet from the organization ' s inside network 192.168.1.0/24. Which IOS command must oe used to create the access control list?

Options:

A.  

B.  

C.  

D.  

Discussion 0
Question # 130

An engineer is configuring Cisco WSA and needs to deploy it in transparent mode. Which configuration component must be used to accomplish this goal?

Options:

A.  

MDA on the router

B.  

PBR on Cisco WSA

C.  

WCCP on switch

D.  

DNS resolution on Cisco WSA

Discussion 0
Question # 131

A logistics company issues corporate laptops that must automatically establish a Cisco Secure Client VPN tunnel whenever users are outside the office and connected to an untrusted external network. Cisco Secure Firewall Threat Defense is the VPN headend and is already configured with remote-access profiles, address pools, and a PKI that distributes both machine and user certificates to endpoints. Management requires the tunnel to come up unattended before any user signs in to a laptop. Device-based authentication must be used, and the client must distinguish the corporate LAN from outside networks. The VPN must be connected when a user is outside the corporate network. Which configuration action must be performed to meet the requirements?

Options:

A.  

Configure a Management VPN tunnel with user-certificate authentication for unattended connectivity.

B.  

Configure Trusted Network Detection and Start Before Login with machine-certificate authentication for the client.

C.  

Configure Trusted Network Detection using cached domain credentials for client authentication.

D.  

Implement Start Before Login paired with user-certificate authentication in the profile.

Discussion 0
Question # 132

A network administrator is setting up Cisco FMC to send logs to Cisco Security Analytics and Logging (SaaS). The network administrator is anticipating a high volume of logging events from the firewalls and wants lo limit the strain on firewall resources. Which method must the administrator use to send these logs to Cisco Security Analytics and Logging?

Options:

A.  

SFTP using the FMCCLI

B.  

syslog using the Secure Event Connector

C.  

direct connection using SNMP traps

D.  

HTTP POST using the Security Analytics FMC plugin

Discussion 0
Question # 133

Which solution allows an administrator to provision, monitor, and secure mobile devices on Windows and Mac computers from a centralized dashboard?

Options:

A.  

Cisco Umbrella

B.  

Cisco AMP for Endpoints

C.  

Cisco ISE

D.  

Cisco Stealthwatch

Discussion 0
Question # 134

What causes alert fatigue in Cisco XDR?

Options:

A.  

Alerts lacking sufficient context to be accurate

B.  

Reauthentication of an active endpoint during a vulnerability incident

C.  

Notifications from too few devices in a data-breach event

D.  

Automatic policy enforcement during a suspicious event

Discussion 0
Question # 135

An organization wants to provide visibility and to identify active threats in its network using a VM. The

organization wants to extract metadata from network packet flow while ensuring that payloads are not retained

or transferred outside the network. Which solution meets these requirements?

Options:

A.  

Cisco Umbrella Cloud

B.  

Cisco Stealthwatch Cloud PNM

C.  

Cisco Stealthwatch Cloud PCM

D.  

Cisco Umbrella On-Premises

Discussion 0

Free Exams Sample Questions

