

Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Practice Questions

Exams4sure Dumps

Exam style questions across every 350-701 domain

Last Update 4 hours ago
Total Questions : 801

Start with our free 350-701 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CCNP Security exam. Each 350-701 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

350-701 PDF

350-701 PDF (Printable)
$54.25
$154.99

350-701 Testing Engine

350-701 PDF (Printable)
$59.5
$169.99

350-701 PDF + Testing Engine

350-701 PDF (Printable)
$74.55
$212.99
Question # 61

Which mitigation strategy should be used to protect against session hijacking attacks in a cloud environment?

Options:

A.  

Implement input validation.

B.  

Use secure cookies.

C.  

Apply the principle of least privilege.

D.  

Use anti-cross-site request forgery tokens.

Discussion 0
Question # 62

What are two functions of IKEv1 but not IKEv2? (Choose two)

Options:

A.  

NAT-T is supported in IKEv1 but rot in IKEv2.

B.  

With IKEv1, when using aggressive mode, the initiator and responder identities are passed cleartext

C.  

With IKEv1, mode negotiates faster than main mode

D.  

IKEv1 uses EAP authentication

E.  

IKEv1 conversations are initiated by the IKE_SA_INIT message

Discussion 0
Question # 63

Which CLI command is used to register a Cisco FirePower sensor to Firepower Management Center?

Options:

A.  

configure system add < host > < key >

B.  

configure manager < key > add host

C.  

configure manager delete

D.  

configure manager add < host > < key

Discussion 0
Question # 64

Which two preventive measures are used to control cross-site scripting? (Choose two)

Options:

A.  

Enable client-side scripts on a per-domain basis.

B.  

Incorporate contextual output encoding/escaping.

C.  

Disable cookie inspection in the HTML inspection engine.

D.  

Run untrusted HTML input through an HTML sanitization engine.

E.  

Same Site cookie attribute should not be used.

Discussion 0
Question # 65

An organization wants to secure users, data, and applications in the cloud. The solution must be API-based and

operate as a cloud-native CAS

B.  

Which solution must be used for this implementation?

Options:

A.  

Cisco Cloudlock

B.  

Cisco Cloud Email Security

C.  

Cisco Firepower Next-Generation Firewall

D.  

Cisco Umbrella

Discussion 0
Question # 66

Which cryptographic process provides origin confidentiality, integrity, and origin authentication for packets?

Options:

A.  

IKEv1

B.  

AH

C.  

ESP

D.  

IKEv2

Discussion 0
Question # 67

What must be enabled to secure SaaS-based applications?

Options:

A.  

modular policy framework

B.  

two-factor authentication

C.  

application security gateway

D.  

end-to-end encryption

Discussion 0
Question # 68

What is an advantage of the Cisco Umbrella roaming client?

Options:

A.  

the ability to see all traffic without requiring TLS decryption

B.  

visibility into IP-based threats by tunneling suspicious IP connections

C.  

the ability to dynamically categorize traffic to previously uncategorized sites

D.  

visibility into traffic that is destined to sites within the office environment

Discussion 0
Question # 69

An administrator is establishing a new site-to-site VPN connection on a Cisco IOS router. The organization

needs to ensure that the ISAKMP key on the hub is used only for terminating traffic from the IP address of

172.19.20.24. Which command on the hub will allow the administrator to accomplish this?

Options:

A.  

crypto ca identity 172.19.20.24

B.  

crypto isakmp key Cisco0123456789 172.19.20.24

C.  

crypto enrollment peer address 172.19.20.24

D.  

crypto isakmp identity address 172.19.20.24

Discussion 0
Question # 70

An engineer needs to detect and quarantine a file named abc424400664 zip based on the MD5 signature of the file using the Outbreak Control list feature within Cisco Advanced Malware Protection (AMP) for Endpoints The configured detection method must work on files of unknown disposition Which Outbreak Control list must be configured to provide this?

Options:

A.  

Blocked Application

B.  

Simple Custom Detection

C.  

Advanced Custom Detection

D.  

Android Custom Detection

Discussion 0
Question # 71

Drag and drop the steps from the left into the correct order on the right to enable AppDynamics to monitor an EC2 instance in Amazon Web Services.
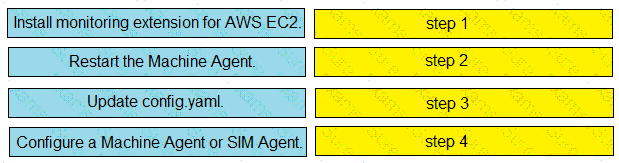
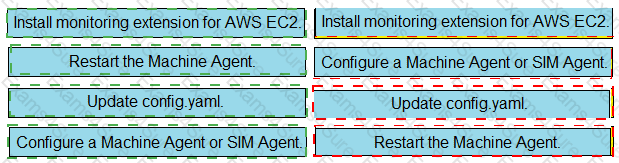
Question # 71

Options:

Discussion 0
Question # 72

An engineer is trying to decide between using L2TP or GRE over IPsec for their site-to-site VPN implementation. What must be un solution?

Options:

A.  

L2TP is an IP packet encapsulation protocol, and GRE over IPsec is a tunneling protocol.

B.  

L2TP uses TCP port 47 and GRE over IPsec uses UDP port 1701.

C.  

GRE over IPsec adds its own header, and L2TP does not.

D.  

GRE over IPsec cannot be used as a standalone protocol, and L2TP can.

Discussion 0
Question # 73

An engineer has been tasked with implementing a solution that can be leveraged for securing the cloud users,

data, and applications. There is a requirement to use the Cisco cloud native CASB and cloud cybersecurity

platform. What should be used to meet these requirements?

Options:

A.  

Cisco Umbrella

B.  

Cisco Cloud Email Security

C.  

Cisco NGFW

D.  

Cisco Cloudlock

Discussion 0
Question # 74

A network engineer must prevent endpoints from becoming infected by malicious files. The infrastructure includes Cisco Secure Endpoint, which must execute suspicious files in a cloud sandbox. Which feature must the engineer configure on Cisco Secure Endpoint to meet the requirement?

Options:

A.  

Dynamic File Analysis

B.  

Orbital Advanced Search

C.  

Layer 4 Traffic Monitor

D.  

Cisco Application Visibility and Control

Discussion 0
Question # 75

What are two differences between a Cisco Secure Web Appliance that is running in transparent mode and one running in explicit mode? (Choose two.)


Options:

A.  

The Cisco Secure Web Appliance responds with its own IP address only if it is running in transparent mode.

B.  

When the Cisco Secure Web Appliance is running in transparent mode, it uses the Secure Web Appliance ' s own IP address as the HTTP request destination.

C.  

The Cisco Secure Web Appliance responds with its own IP address only if it is running in explicit mode.

D.  

The Cisco Secure Web Appliance is configured in a web browser only if it is running in transparent mode.

E.  

The Cisco Secure Web Appliance uses a Layer 3 device to redirect traffic only if it is running in transparent mode.

Discussion 0

Free Exams Sample Questions
