

Exam style questions across every 350-701 domain
Last Update 5 hours ago
Total Questions : 801
Start with our free 350-701 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CCNP Security exam. Each 350-701 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

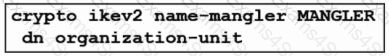
Refer to the exhibit. An engineer is implementing a certificate-based VPN. What is the result of the existing configuration?
An engineer is implementing DHCP security mechanisms and needs the ability to add additional attributes to profiles that are created within Cisco ISE Which action accomplishes this task?
Which IPS analysis technique matches traffic against a database of known attack patterns?
An engineer is trying to decide whether to use Cisco Umbrella, Cisco CloudLock, Cisco Stealthwatch, or Cisco AppDynamics Cloud Monitoring for visibility into data transfers as well as protection against data exfiltration Which solution best meets these requirements?
Which technology provides a combination of endpoint protection endpoint detection, and response?
What is a functional difference between Cisco AMP for Endpoints and Cisco Umbrella Roaming Client?
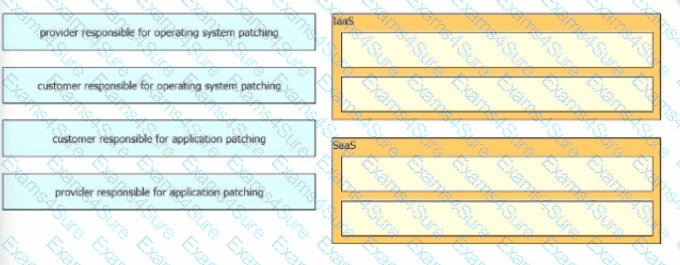
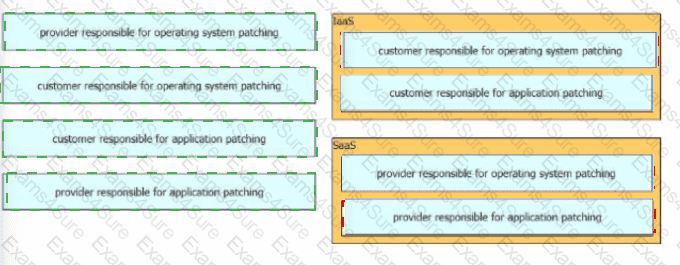
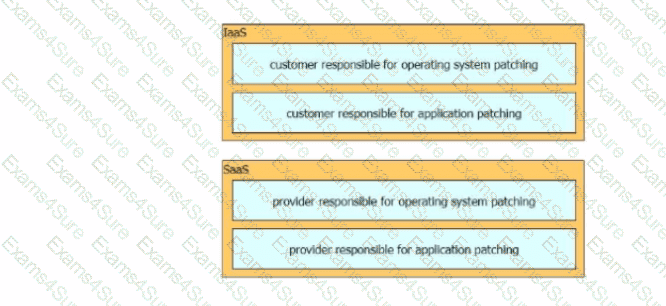
Drag and drop the security responsibilities from the left onto the corresponding cloud service models on the right.
A pharmaceutical research facility has implemented a “Clean Room” network segment to protect sensitive research data and automated manufacturing equipment. Strict compliance requirements mandate that all network traffic logs from the Cisco Secure Firewall serving the segment be forwarded to Splunk for auditing. A Splunk Universal Forwarder is deployed locally on the log-collection servers to monitor syslog files. The engineer must configure the Universal Forwarder to monitor the local syslog files and assign a specific source type for proper ingestion into Splunk. Which stanza configuration must be used to meet the requirements?
Which system facilitates deploying microsegmentation and multi-tenancy services with a policy-based container?



