Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Practice Questions

Exams4sure Dumps

Exam style questions across every 350-701 domain

Last Update 6 hours ago
Total Questions : 801

Start with our free 350-701 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CCNP Security exam. Each 350-701 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

350-701 PDF

350-701 PDF (Printable)
$54.25
$154.99

350-701 Testing Engine

350-701 PDF (Printable)
$59.5
$169.99

350-701 PDF + Testing Engine

350-701 PDF (Printable)
$74.55
$212.99
Question # 211

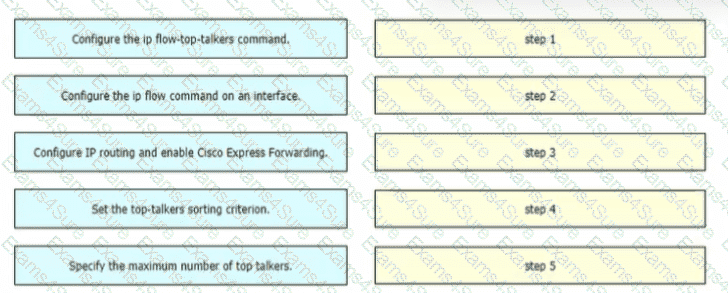
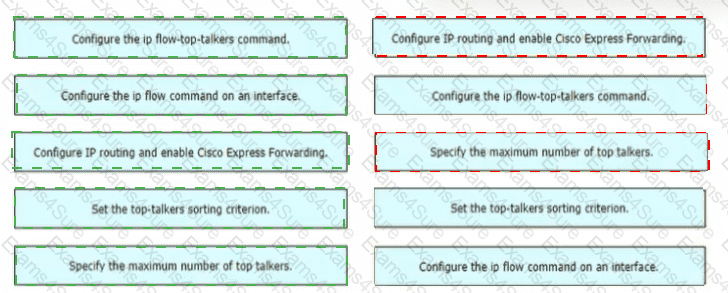
A network engineer is configuring NetFlow top talkers on a Cisco router Drag and drop the steps in the process from the left into the sequence on the right
Question # 211

Options:

Discussion 0
Question # 212

Which two characteristics of messenger protocols make data exfiltration difficult to detect and prevent?

(Choose two)

Options:

A.  

Outgoing traffic is allowed so users can communicate with outside organizations.

B.  

Malware infects the messenger application on the user endpoint to send company data.

C.  

Traffic is encrypted, which prevents visibility on firewalls and IPS systems.

D.  

An exposed API for the messaging platform is used to send large amounts of data.

E.  

Messenger applications cannot be segmented with standard network controls

Discussion 0
Question # 213

What is the difference between deceptive phishing and spear phishing?

Options:

A.  

Deceptive phishing is an attacked aimed at a specific user in the organization who holds a C-level role.

B.  

A spear phishing campaign is aimed at a specific person versus a group of people.

C.  

Spear phishing is when the attack is aimed at the C-level executives of an organization.

D.  

Deceptive phishing hijacks and manipulates the DNS server of the victim and redirects the user to a false webpage.

Discussion 0
Question # 214

Which Cisco security solution determines if an endpoint has the latest OS updates and patches installed on the system?

Options:

A.  

Cisco Endpoint Security Analytics

B.  

Cisco AMP for Endpoints

C.  

Endpoint Compliance Scanner

D.  

Security Posture Assessment Service

Discussion 0
Question # 215

What is a characteristic of traffic storm control behavior?

Options:

A.  

Traffic storm control drops all broadcast and multicast traffic if the combined traffic exceeds the level withinthe interval.

B.  

Traffic storm control cannot determine if the packet is unicast or broadcast.

C.  

Traffic storm control monitors incoming traffic levels over a 10-second traffic storm control interval.

D.  

Traffic storm control uses the Individual/Group bit in the packet source address to determine if the packet isunicast or broadcast.

Discussion 0
Question # 216

Which policy is used to capture host information on the Cisco Firepower Next Generation Intrusion Prevention

System?

Options:

A.  

Correlation

B.  

Intrusion

C.  

Access Control

D.  

Network Discovery

Discussion 0
Question # 217

A security engineer must configure a Splunk Universal Forwarder to send network traffic logs from Cisco Catalyst switches to a Splunk indexer cluster. Strict compliance requirements require all network traffic logs to be ingested into Splunk as an audit trail. The environment includes thousands of forwarders, and the data must be distributed across all indexers. Which two configuration actions must be performed? (Choose two.)

Options:

A.  

Configure outputs.conf with the DNS names and indexing ports of all indexers within the cluster.

B.  

Implement a large output queue in outputs.conf and disable automatic load balancing.

C.  

Configure the forwarder to write logs to a local file share and schedule a batch job to copy the data into the indexers.

D.  

Use a deployment server to push an application containing outputs.conf to all Universal Forwarders.

E.  

Configure a single primary indexer in outputs.conf and enable a forced connection.

Discussion 0
Question # 218

Which solution offers automated blocking of known threats and visibility into zero-day attack behavior, with the ability to respond directly from the console?

Options:

A.  

EPP solution with an HIDS integration

B.  

Cloud-native antivirus with offline update support

C.  

EDR with behavioral analytics and remote containment

D.  

Secure Email Gateway with phishing sandboxing

Discussion 0
Question # 219

Which security control is required for identifying and neutralizing malicious code that attempts to execute on an endpoint?

Options:

A.  

EPP

B.  

XDR

C.  

SWG

D.  

CASB

Discussion 0
Question # 220

Which Cisco command enables authentication, authorization, and accounting globally so that CoA is supported on the device?

Options:

A.  

aaa server radius dynamic-author

B.  

aaa new-model

C.  

auth-type all

D.  

ip device-tracking

Discussion 0
Question # 221

An engineer configured a new network identity in Cisco Umbrella but must verify that traffic is being routed

through the Cisco Umbrella network. Which action tests the routing?

Options:

A.  

Ensure that the client computers are pointing to the on-premises DNS servers.

B.  

Enable the Intelligent Proxy to validate that traffic is being routed correctly.

C.  

Add the public IP address that the client computers are behind to a Core Identity.

D.  

Browse to http://welcome.umbrella.com/ to validate that the new identity is working.

Discussion 0
Question # 222

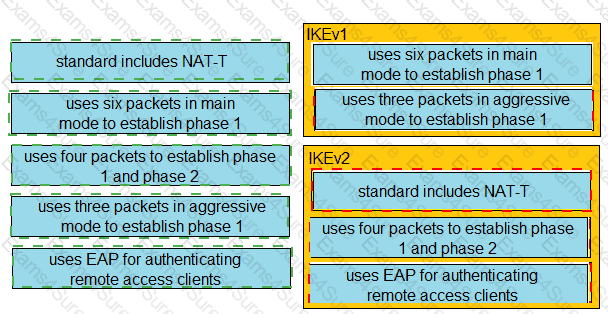
Drag and drop the descriptions from the left onto the correct protocol versions on the right.
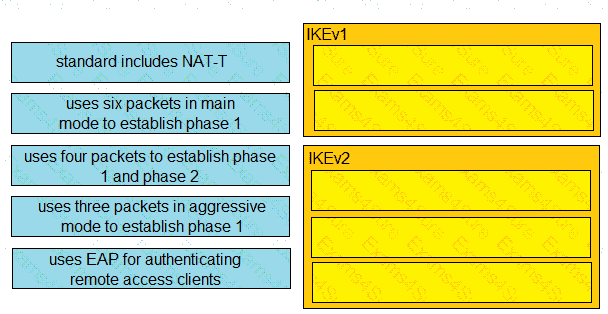
Question # 222

Options:

Discussion 0
Question # 223

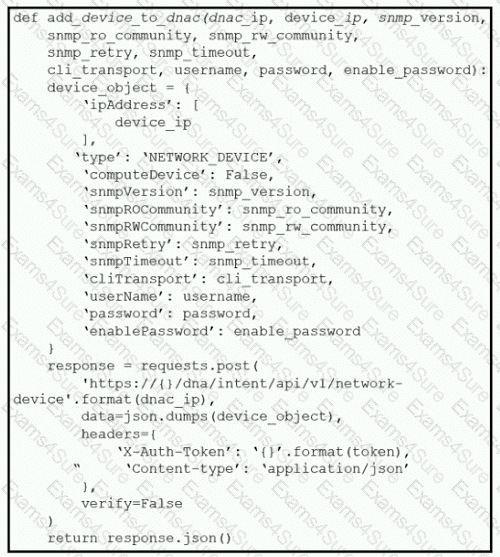
Refer to the exhibit.

Question # 223

What is the result of this Python script of the Cisco DNA Center API?

Options:

A.  

adds authentication to a switch

B.  

adds a switch to Cisco DNA Center

C.  

receives information about a switch

D.  

deletes a switch from Cisco DNA Center

Discussion 0
Question # 224

A network engineer is deciding whether to use stateful or stateless failover when configuring two ASAs for high availability. What is the connection status in both cases?

Options:

A.  

need to be reestablished with stateful failover and preserved with stateless failover

B.  

preserved with stateful failover and need to be reestablished with stateless failover

C.  

preserved with both stateful and stateless failover

D.  

need to be reestablished with both stateful and stateless failover

Discussion 0
Question # 225

A security engineer is deploying an IPsec site-to-site VPN between headquarters and a remote plant, protected by Cisco Secure Firewall Threat Defense managed by Cisco Secure Firewall Management Center. The following configurations have already been completed:

    Matching IKEv2 proposals, preshared keys, and IPsec transform sets

    Access control rules permitting the traffic

    Crypto maps applied to the outside interfaces

    VPN traffic exempted from inspection

During a packet capture on the firewall, the engineer observes that the traffic is translated to the public IP address, preventing tunnel establishment. Which configuration action must be performed next?


Options:

A.  

Configure NAT exemption for traffic between the interesting subnet pairs.

B.  

Create a tunnel group with preshared-key authentication under connection profiles.

C.  

Enable IKEv2 fragmentation on both peers to reduce packet size.

D.  

Attach the new VPN policy to the global prefilter default action.

Discussion 0

Free Exams Sample Questions