

Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Practice Questions

Exams4sure Dumps

Exam style questions across every 350-701 domain

Last Update 7 hours ago
Total Questions : 801

Start with our free 350-701 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CCNP Security exam. Each 350-701 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

350-701 PDF

350-701 PDF (Printable)
$54.25
$154.99

350-701 Testing Engine

350-701 PDF (Printable)
$59.5
$169.99

350-701 PDF + Testing Engine

350-701 PDF (Printable)
$74.55
$212.99
Question # 226

What is the purpose of the Trusted Automated exchange cyber threat intelligence industry standard?

Options:

A.  

public collection of threat intelligence feeds

B.  

threat intelligence sharing organization

C.  

language used to represent security information

D.  

service used to exchange security information

Discussion 0
Question # 227

Which two request methods of REST API are valid on the Cisco ASA Platform? (Choose two.)

Options:

A.  

GET

B.  

CONNECT

C.  

PUSH

D.  

OPTIONS

E.  

PUT

Discussion 0
Question # 228

An engineer must configure Cisco AMP for Endpoints so that it contains a list of files that should not be executed by users. These files must not be quarantined. Which action meets this configuration requirement?

Options:

A.  

Identity the network IPs and place them in a blocked list.

B.  

Modify the advanced custom detection list to include these files.

C.  

Create an application control blocked applications list.

D.  

Add a list for simple custom detection.

Discussion 0
Question # 229

Which security solution uses NetFlow to provide visibility across the network, data center, branch offices, and cloud?

Options:

A.  

Cisco CTA

B.  

Cisco Encrypted Traffic Analytics

C.  

Cisco Umbrella

D.  

Cisco Secure Network Analytics

Discussion 0
Question # 230

For a given policy in Cisco Umbrella, how should a customer block website based on a custom list?

Options:

A.  

by specifying blocked domains in me policy settings

B.  

by specifying the websites in a custom blocked category

C.  

by adding the websites to a blocked type destination list

D.  

by adding the website IP addresses to the Cisco Umbrella blocklist

Discussion 0
Question # 231

An organization wants to use Cisco FTD or Cisco ASA devices. Specific URLs must be blocked from being

accessed via the firewall which requires that the administrator input the bad URL categories that the

organization wants blocked into the access policy. Which solution should be used to meet this requirement?
Options:

A.  

Cisco ASA because it enables URL filtering and blocks malicious URLs by default, whereas Cisco FTDdoes not

B.  

Cisco ASA because it includes URL filtering in the access control policy capabilities, whereas Cisco FTD does not

C.  

Cisco FTD because it includes URL filtering in the access control policy capabilities, whereas Cisco ASA does not

D.  

Cisco FTD because it enables URL filtering and blocks malicious URLs by default, whereas Cisco ASA does not

Discussion 0
Question # 232

Question # 232

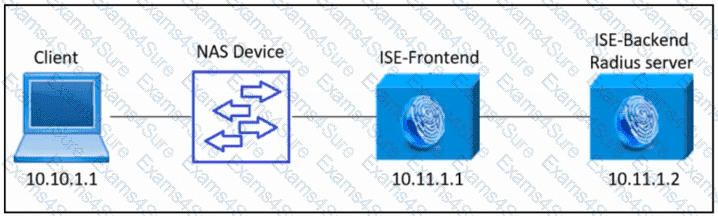
Refer to the exhibit. An engineer must configure a new Cisco ISE backend server as a RADIUS server to provide AAA for all access requests from the client to the ISE-Frontend server.

Which Cisco ISE configuration must be used?

Options:

A.  

Set 10.11.1.2 as a network device in ISE-Frontend. Set port 1700/2083 for RADIUS authentication.

B.  

Set 10.11.1.1 as the external RADIUS server in ISE-Frontend. Set ports 1812/1813 for authentication and accounting.

C.  

Set 10.11.1.2 as the external RADIUS server in ISE-Frontend. Set ports 1812/1813 for authentication and accounting.

D.  

Set 10.11.1.1 as a network device in ISE-Frontend. Set ports 1700/2083 for RADIUS authentication.

Discussion 0
Question # 233

When wired 802.1X authentication is implemented, which two components are required? (Choose two)

Options:

A.  

authentication server: Cisco Identity Service Engine

B.  

supplicant: Cisco AnyConnect ISE Posture module

C.  

authenticator: Cisco Catalyst switch

D.  

authenticator: Cisco Identity Services Engine

E.  

authentication server: Cisco Prime Infrastructure

Discussion 0
Question # 234

What are two things to consider when using PAC files with the Cisco WSA? (Choose two.)

Options:

A.  

If the WSA host port is changed, the default port redirects web traffic to the correct port automatically.

B.  

PAC files use if-else statements to determine whether to use a proxy or a direct connection for traffic between the PC and the host.

C.  

The WSA hosts PAC files on port 9001 by default.

D.  

The WSA hosts PAC files on port 6001 by default.

E.  

By default, they direct traffic through a proxy when the PC and the host are on the same subnet.

Discussion 0
Question # 235

Which Cisco solution does Cisco Umbrella integrate with to determine if a URL is malicious?

Options:

A.  

AMP

B.  

AnyConnect

C.  

DynDNS

D.  

Talos

Discussion 0
Question # 236

An engineer needs to configure an access control policy rule to always send traffic for inspection without

using the default action. Which action should be configured for this rule?

Options:

A.  

monitor

B.  

allow

C.  

block

D.  

trust

Discussion 0
Question # 237

A security engineer must create a policy based on the reputation verdict of a file from a Cisco Secure Email Gateway. The file with an undetermined verdict must be dropped. Which action must the security engineer take to meet the requirement?


Options:

A.  

Configure threshold settings for files with no score to be allowed.

B.  

Set up a policy to automatically drop files with no reputation score.

C.  

Implement a policy to disable file analysis.

D.  

Create a policy to send a file to quarantine.

Discussion 0
Question # 238

Which Cisco security solution stops exfiltration using HTTPS?

Options:

A.  

Cisco FTD

B.  

Cisco AnyConnect

C.  

Cisco CTA

D.  

Cisco ASA

Discussion 0
Question # 239

Which role is a default guest type in Cisco ISE?

Options:

A.  

Monthly

B.  

Yearly

C.  

Contractor

D.  

Full-Time

Discussion 0
Question # 240

Which type of encryption uses a public key and private key?

Options:

A.  

Asymmetric

B.  

Symmetric

C.  

Linear

D.  

Nonlinear

Discussion 0

Free Exams Sample Questions
